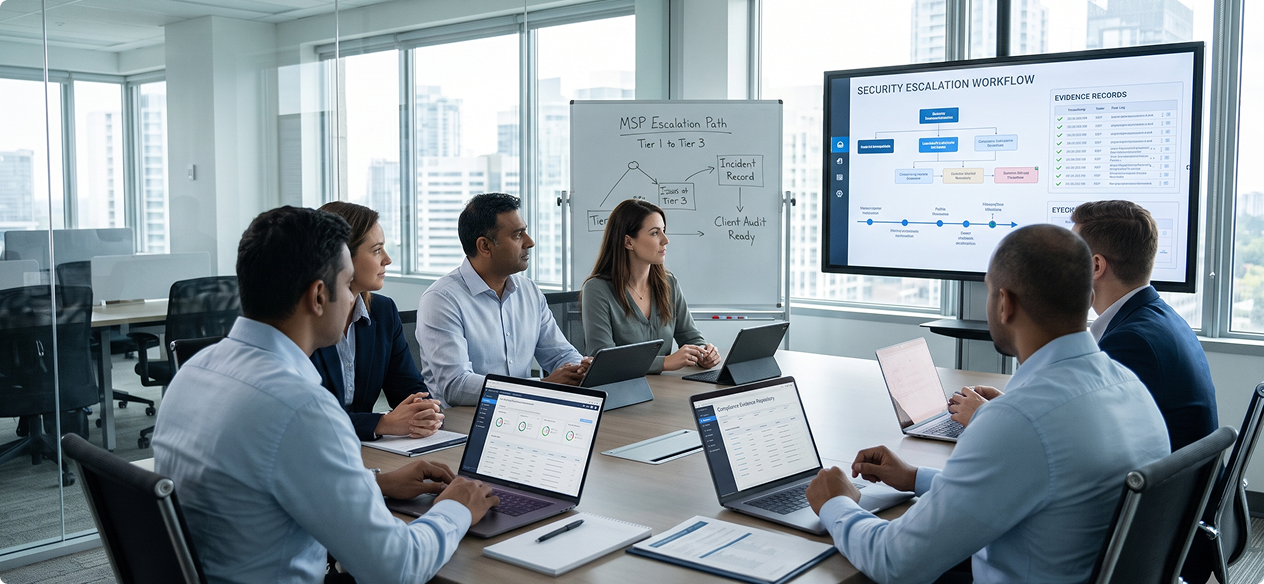
The client is a U.S.-based Managed Service Provider (MSP) supporting approximately 900 endpoints across 30 professional-services and healthcare small and midsize business clients.
Its internal team manages security tools across client environments, supported by an MSP-appointed security lead and an approved incident-response provider. However, responsibility for reviewing alerts and preserving evidence varies across clients, and some incidents are investigated in chat without a complete record.
For clients handling sensitive information, reconstructing who approved an action or when a client was notified became increasingly challenging. The business needed a documented escalation and evidence process rather than additional monitoring alone.
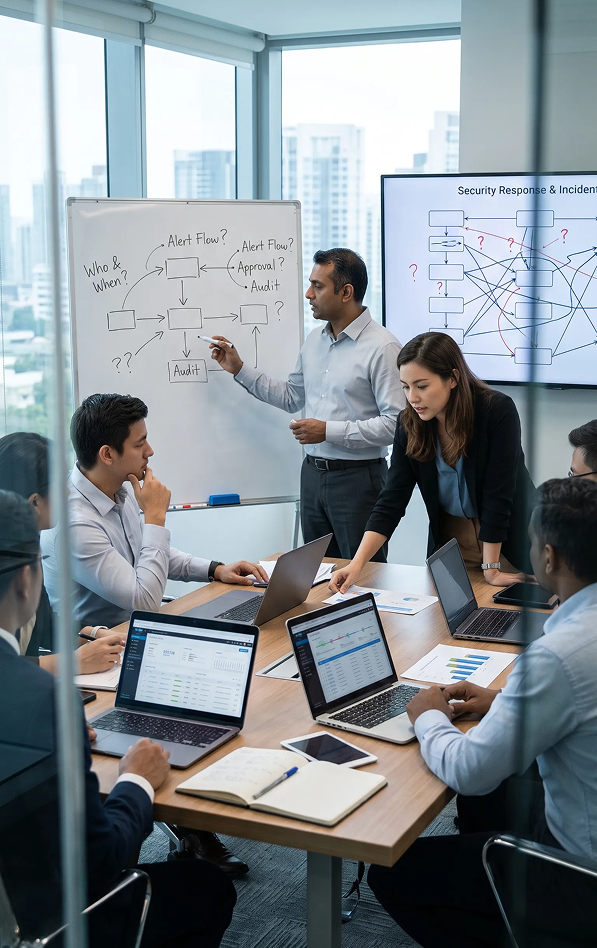
Responsibility for reviewing security alerts varied across clients.
Some notifications reached engineers without enough information to act.
Investigations held in chat left gaps in the formal record.
Records did not show who approved actions or when clients were notified.
Unclear access rights could undermine an investigation or audit.
Roles for SOC analysis, forensics, and incident command were not explicit.
Paired NOC analysts with a named security escalation lead, with SOC analysis, forensics, and incident command assigned explicitly by capability and contract scope.
Inventoried approved log sources and introduced daily checks to confirm that required sources were reporting as expected.
Documented escalation contacts for each client and rehearsed alert-to-incident workflows before they were needed in a live incident.
Validated high-severity alerts and escalated them through an acknowledged paging path, with backup contacts for any missed acknowledgment.
Preserved timestamps, event references, decisions, and actions in the PSA or security case system, with analyst actions logged for reconstruction.
Limited endpoint isolation, account disabling, and other disruptive actions to preauthorized conditions or incident-commander approval.
Minimized sensitive content, used approved storage, and enforced retention and deletion policies, with tenant-scoped and time-limited privileged access.
Tested access rights and escalation procedures through access reviews and tabletop exercises before they were needed in a live crisis.
| Operational Metric | Before | After |
|---|---|---|
| Required log-source reporting coverage | 78% | 95% |
| Controlled detection latency p90 | 35 minutes | 10 minute |
| Critical alert human-acknowledgment p90 | 28 minutes | 15 minutes |
| Validated critical incident escalation p90 | 45 minutes | 15 minutes |
| Authorized containment execution p90 | 50 minutes | 30 minutes |
| Complete incident evidence records | 62% | 95% |
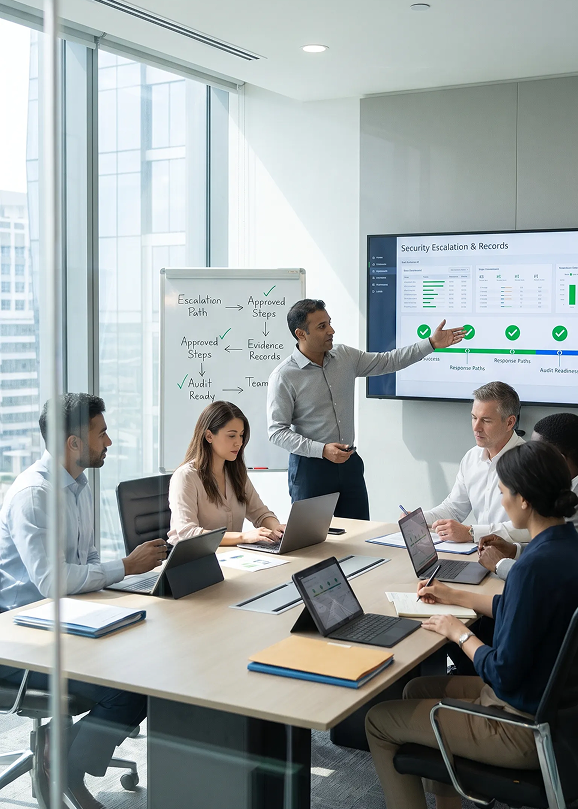
Established named escalation contacts, explicit response roles, and backup paging for every client, reducing confusion during high-severity alerts.
Maintained timestamped decisions, approvals, and evidence references in a single system of record, making investigations easier to reconstruct.
Kept disruptive actions within preauthorized conditions or incident-commander approval, protecting client operations from unplanned changes.
Provided consistent documentation and control evidence to support client audits, while legal and compliance decisions remained with the MSP.
Established a repeatable escalation model to help support regulated clients without relying exclusively on additional internal security hires.
Increased the share of required log sources reporting as expected from 78% to 95%.
Reduced p90 detection latency in matched controlled tests from 35 to 10 minutes.
Reduced p90 time from validation to acceptance by the authorized incident lead from 45 to 15 minutes.
Reduced p90 time from approval to completed containment in exercises from 50 to 30 minutes.
Increased the share of incident records meeting the fixed evidence checklist from 62% to 95%.
“Defining our security escalation process has helped us establish a more structured approach to incident handling. Named escalation contacts, consistent evidence records, and clear approval trails have made it easier for our team to reconstruct decisions and respond to evidence requests.”
Security escalation support provides alert validation, evidence preservation, and escalation of critical incidents to an authorized incident lead. It helps MSPs maintain clear ownership of security events across clients.
NOC and security escalation support enables MSPs to strengthen security operations while retaining ownership of client communications and legal notification decisions. The team works within agreed escalation paths, approval rules, and evidence standards.
Yes. Escalation support can use an MSP’s existing SIEM, endpoint, identity, PSA, and documentation platforms, provided licensing, sensor coverage, retention, and operating ownership are confirmed.
Depending on the agreed scope, a NOC team can validate alerts, preserve evidence, page the security lead, and execute preauthorized containment. Full SOC analysis, forensics, and incident command are assigned explicitly.
A documented process records who reviewed an alert, who approved each action, and when clients were notified. This makes investigation records easier to reconstruct and review.
Escalation times depend on the MSP’s severity definitions and contract scope. A 15-minute p90 from validation to incident-lead acceptance can help set expectations, provided pre-validation delay is reported separately.
Detection latency measures the time from a test event to a generated alert in controlled tests. Attacker dwell time measures how long a real threat remains undetected in an environment.
MSPs should track log-source coverage, detection latency, acknowledgment and escalation times, containment execution, and evidence record completeness. Exercise results should never be merged with production incident statistics.
No. Compliance-ready support improves documentation and control evidence, but compliance depends on legal review, applicable obligations, client agreements, and assessment by counsel and security owners.
An MSP should evaluate response boundaries, SOC and forensic capabilities, escalation procedures, containment authority, access controls, evidence handling, reporting methods, and total operating costs.
Effective security operations require more than monitoring tools. They require defined response boundaries, documented escalation paths, complete evidence records, and operational accountability.
Moksh Tech helps MSPs strengthen service delivery through 24/7 NOC services and Managed IT Support Services in the USA.
Explore how the right escalation model can help your team close logging gaps, clarify authorized actions, and support regulated client requirements.