The client is a U.S.-based Managed Service Provider (MSP) supporting 1,000 managed Windows endpoints across 35 small and midsize business clients, including remote devices and business-critical workstations.
Its support team manages patch deployment through its RMM and endpoint tools. However, the patch dashboard only reflects devices that check in, leaving offline laptops and pending restarts outside the team’s attention.
Without visibility of every device, explaining residual risk confidently during client reviews became increasingly challenging. The business needed ownership of the full patch lifecycle rather than another deployment schedule.
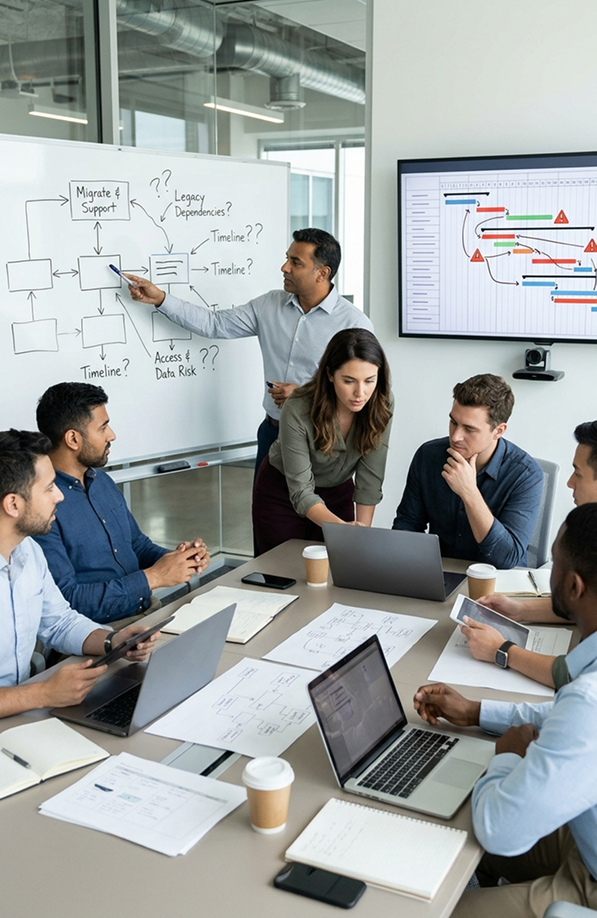
Offline laptops and pending restarts were missing from the dashboard.
Different tools applied overlapping patch policies to the same devices.
Unsupported devices were blended into the same compliance summary.
Installation, restart, and completion were not tracked separately.
Repeated patch exceptions consumed senior engineering time.
Unexpected restarts could disrupt users.
Assigned an endpoint operations engineer with NOC oversight, working alongside an MSP change approver for every rollout.
Reconciled the device inventory during a four-week cleanup, assigning each endpoint a policy and flagging unsupported systems, stale agents, and approved exceptions.
Assigned one policy authority for each update workload to prevent conflicting RMM and Intune controls, with tool telemetry verifying completion.
Deployed updates through pilot and production rings aligned to client maintenance windows, pausing the affected ring for approved rollback if an update caused an incident.
Converted failed deployments into tickets with error details and a named owner, tracking unique devices rather than repeated attempts.
Issued restart reminders under the MSP's approved communication and user-impact policy, giving users advance notice.
Routed critical exploitable vulnerabilities through a separate risk review and expedited path instead of the normal monthly cycle.
Tracked install success, restart state, and post-update health, with weekly reports exposing excluded, offline, and exception devices

| Operational Metric | Before | After |
|---|---|---|
| Monthly policy patch compliance | 820 of 1,000 endpoints | 950 of 1,000 endpoints |
| Endpoints with overdue restarts | 110 | 30 |
| Unresolved deployment failures older than seven days | 85 endpoints | 25 endpoints |
| Stale endpoint telemetry over seven days | 90 endpoints | 30 endpoints |
| Exceptions with owner and expiry | 12 of 40 | 40 of 40 |
Kept offline, excluded, and exception devices in reporting, giving account managers an accurate view of the full endpoint estate.
Moved failure follow-up into owned tickets with clear error details, reducing the senior support time spent chasing repeated exceptions.
Aligned rollouts and restart reminders with client maintenance windows and approved communication policies.
Provided weekly reports that separated compliance, exceptions, and residual risk, giving account managers a clear basis for client decisions.
Established a repeatable patch lifecycle to help manage growing endpoint counts without relying exclusively on additional internal hires.
Increased endpoints meeting the 14-day deadline from 820 to 950 of 1,000, with offline devices counted.
Reduced endpoints with overdue restarts from 110 to 30.
Reduced unresolved failures older than seven days from 85 to 25 endpoints.
Reduced endpoints without a check-in for over seven days from 90 to 30.
Increased exceptions with a named owner and expiry from 12 of 40 to 40 of 40.
“Bringing structure to our patch operations has helped us establish a more transparent approach to client reviews. Visible exceptions, owned failure tickets, and verified completion have made it easier for our account managers to explain patch status and residual risk with confidence.”
Patch management for MSPs covers policy assignment, staged deployment, restart management, failure follow-up, and verified completion across client endpoints. It helps MSPs keep devices current while managing exceptions.
Outsourced patch management enables MSPs to extend endpoint capacity while retaining ownership of change approval and client relationships. The team works within agreed policies, maintenance windows, and communication standards.
Yes. Patch operations can use an MSP’s existing RMM, Intune, endpoint security, and PSA platforms, provided product functionality and responsibilities are validated for the device estate.
Depending on the agreed scope, a patch team can reconcile inventory, assign policies, run ring-based rollouts, manage restart reminders, follow up failures, pause rings for approved rollback, and report exceptions.
Failed deployments become owned tickets with error details, and exceptions are tracked in an approved register. This reduces the time senior engineers spend chasing repeated failures, while restart and exception status stays visible in weekly reports.
Timelines depend on exploitability, client constraints, and the MSP’s risk policy. Critical exploitable vulnerabilities should follow an expedited path with a separate risk review rather than waiting for the monthly cycle.
Installation means an update was applied to a device. Verified completion confirms the update installed, the device restarted, and post-update health checks passed.
MSPs should track policy compliance, overdue restarts, aged deployment failures, stale telemetry, and documented exceptions. Offline devices should stay in the denominator, and comparisons should use a fixed endpoint cohort across matched monthly cycles.
No. Patch compliance shows operating system update status, but application updates, firmware, unsupported systems, and compensating controls need separate coverage. Approved exceptions should never be classified as patched.
An MSP should evaluate inventory practices, policy ownership, rollout rings, restart policies, exception handling, rollback plans, reporting methods, and total operating costs.
Reliable patching requires more than a deployment schedule. It requires accurate inventory, clear policy ownership, visible exceptions, and verified completion.
Moksh Tech helps MSPs strengthen service delivery through 24/7 NOC services and Managed IT Support Services in the USA.
Explore how the right patch model can help your team improve inventory quality, respect maintenance windows, and define what a completed update means.